A business form can connect public visitors with private records, uploaded files and external services. Its visible design is only one part of the control. Secret storage, server-side validation, permissions and failure recovery determine how the application handles information.
This guide explains the decisions to review with an authorised developer. It focuses on dependable enquiry and application workflows rather than assuming that a widget or private-looking address proves protection.
Identify secrets and their owners
API keys, signing secrets and service credentials should have a defined purpose, owner and access scope. Record where they are used without placing the values in routine documentation. An integration register should help locate the approved storage mechanism and recovery process.
Keep secrets out of public source code, client-side scripts and shared error reports. Choose storage supported by the actual environment, with appropriate retrieval permissions and audit arrangements. A folder described as private is not sufficient evidence that access is controlled.
Plan the credential lifecycle
Establish how a credential is issued, changed, revoked and replaced if exposed. Identify dependent applications before a planned rotation, so the change can be coordinated and verified. Limit the time and scope of overlapping credentials to what the supported process needs.
Check that logs, exports and backups do not accidentally expose the value to unrelated users. Where a service identity can use a supported mechanism without an embedded credential, assess it on its actual capabilities. The correct arrangement depends on the platform and workflow.
Ask for uploads only when they help the task
Explain why an attachment is needed and whether the enquiry can proceed without it. A customer requesting a quotation may be able to provide a description first. Avoid collecting documents simply because the form supports an upload control.
State accepted types and limits before selection. Provide useful errors for unsupported files or failed transfers and preserve other entered information where practical. Check keyboard operation and the customer's ability to remove or replace a selected file.
Validate files beyond the displayed name
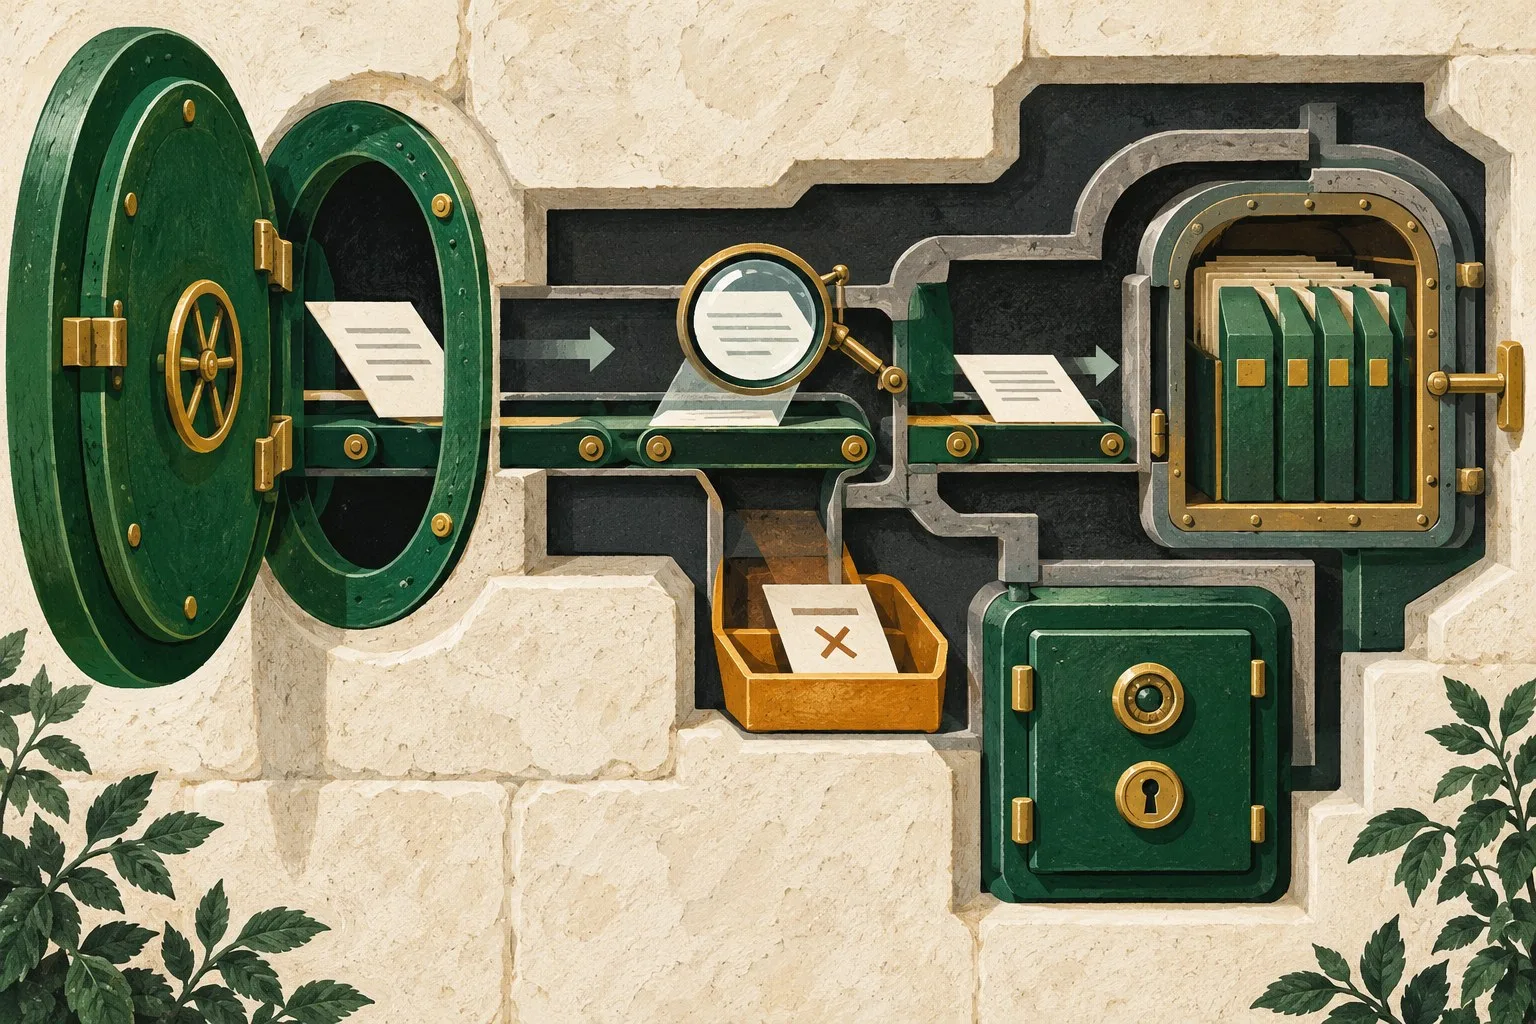
Use a defined allow-list suited to the business requirement and verify the file through appropriate server-side checks. A filename extension or browser-provided content type alone can be misleading. Consider size, contents, processing risks and the tools that will read the file.
Rename stored files through a safe strategy and keep their business relationship clear. Avoid executing uploaded material as application code. If archives or document conversions are supported, assess expanded size and processing behaviour rather than applying only an initial upload limit.
Control storage and retrieval
Where appropriate, store uploads separately from the public web area and serve them through an authorised access path. Check the effective permissions for the application, staff and visitors. An address that is difficult to guess does not establish that a file is private.
Verify that a user cannot obtain another customer's attachment by changing an identifier. Include preview, download, sharing and deletion paths in the review. Decide how files are retained and removed, including relevant copies and recovery arrangements.
Review scanning and external processing
If a scanning or conversion service is used, establish what information is sent, where processing happens and what is retained. Uploading a confidential file to a public analysis service can create an unnecessary disclosure. Select an approved method suitable for the data and service requirement.
Define what happens while a file is awaiting a result and what staff can do if processing fails. A successful upload acknowledgement should not imply that a file has already passed every required check. Keep the state visible enough to support the workflow.
Validate anti-spam challenges on the server
A verification widget must be connected to the supported server-side validation process. Confirm the required secret, expected destination and response handling. The widget's appearance alone does not prove that a submitted request is being checked.
Tokens can expire or be single-use. As reviewed on 11 October 2026, Turnstile tokens have a five-minute validity period and are single-use. Build an appropriate refresh and recovery path for a customer who pauses. A failed or expired token does not by itself establish malicious intent.
Request device permissions in context
If an application needs camera, location or notification access, ask when the relevant feature is used and explain its purpose. Provide an appropriate path when permission is denied. Operating systems and browsers have different permission behaviour, so test the actual supported devices.
- Confirm secret values remain outside public responses and logs.
- Test valid, invalid, oversized and interrupted uploads.
- Verify attachment access for different users and roles.
- Check expired verification and safe form recovery.
- Confirm staff ownership of unresolved exceptions.
Our account access guide complements this review. Giraffe Digital's website design service can connect the form's customer experience with its application and operational requirements.