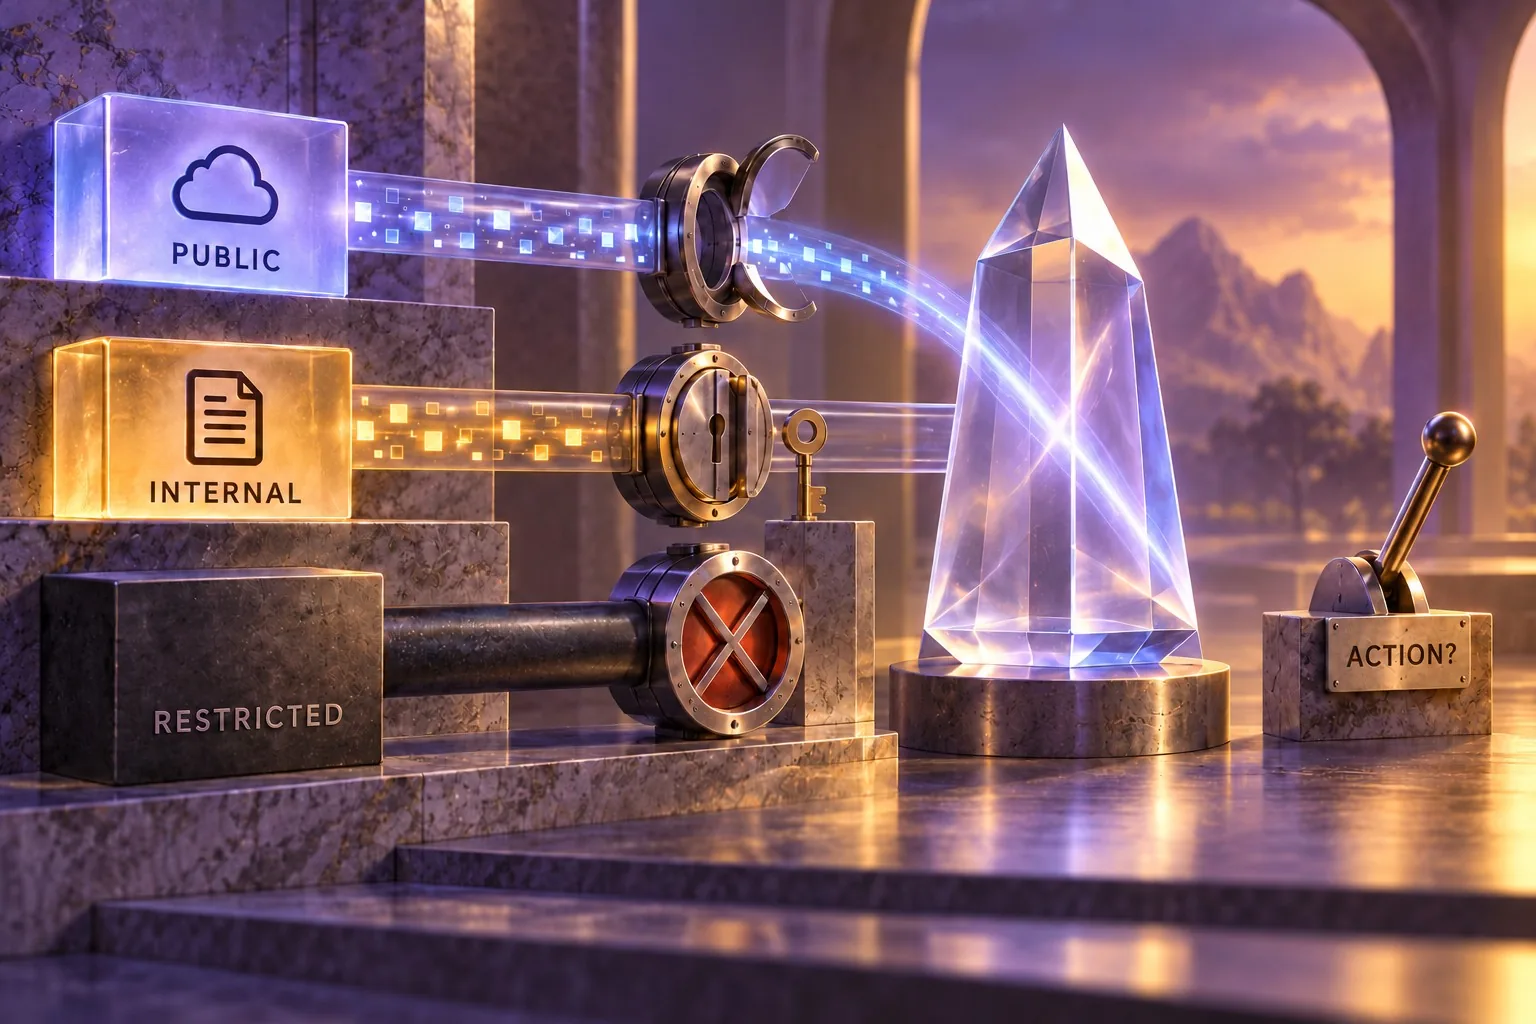
An AI assistant can only be useful with the right information, but connecting it to every business document is rarely a sensible starting point. Public service descriptions, internal procedures, client records and commercial negotiations have different purposes and audiences. An access plan needs to reflect those differences before the assistant begins answering questions.
The first decision is therefore what the assistant is meant to do. A public website assistant that explains services needs a different information boundary from an internal assistant helping an authorised account manager. This guide explains how to create a practical information access brief, agree ownership and test whether the implemented system respects those decisions.
Define the assistant's work and audience
Describe a few useful tasks. For example, a website assistant could explain published service options and direct visitors to the relevant enquiry page. An internal assistant could help a team find approved operating instructions. Write the intended users and expected outputs beside each task.
Avoid starting with a broad ambition such as “answer any business question”. That makes it difficult to judge whether a document is necessary or whether an answer is appropriate. A clearer task lets the team ask which sources are needed, which facts must remain current and who should approve the resulting information.
Distinguish finding information from making a decision. An assistant that summarises an approved process does not automatically have authority to offer a discount, accept a contractual change or make a commitment to a customer. Record where a person needs to take over. The information access brief and the assistant's permitted actions should support the same operating purpose.
Build a source register before connecting documents
List the proposed sources with a named business owner. For each one, record its purpose, intended audience, current location and review arrangements. Include whether it is an approved source or a working draft. The register should explain why the assistant needs the source, not simply why somebody can locate it.
Consider a service information folder containing published descriptions, draft pricing, client examples and internal discussions. Treating the whole folder as one approved source would hide important differences. Prepare a smaller collection of approved material for the task, or organise the sources so the relevant access rules can be implemented and verified.
Ask the owner to identify material that should be excluded. Old proposals, private notes and unapproved estimates may contain accurate facts in one context while being unsuitable for the assistant's audience. The process should not rely on the assistant guessing which parts of a mixed document can be shared.
Separate public information from internal working material
A public assistant should have a clear set of information approved for public use. Useful material might include published service explanations, contact routes and agreed answers to common questions. Keep the collection aligned with the website so the assistant does not describe a service or availability that the business no longer offers.
An internal assistant needs a more detailed audience definition. “Staff” may include several roles with different access to client, finance or personnel information. Write specific examples of what each intended role may retrieve. Where client records are involved, include examples that distinguish one client's information from another's.
Review personal and confidential information with the person responsible for your policies and information handling. Document the approved purpose, the minimum information needed and the relevant operating arrangements. This article provides a planning method; your organisation's actual permissions, contractual commitments and policies need their own review by the appropriate people.
Require access controls outside the assistant's wording
Limit an assistant's privileges and enforce authorisation outside the model. Treat retrieved material as untrusted input. A written instruction telling the assistant to keep information private is insufficient as the access control for confidential sources. Our AI agent tools and access controls guide provides the related checks.
Ask the developer to show how the authenticated user's permissions determine retrieval before restricted content reaches the model. Also ask how tool calls are checked against that user's authority. The demonstration should include denied requests, rather than only successful examples. The business needs evidence that the implemented boundary matches the approved register.
Record access and action permissions separately. A person may be allowed to read an approved document without being allowed to edit it or send its contents elsewhere. Give the assistant only the tool capabilities required for its task, and define approval steps for consequential actions. Review this design with the technical owner rather than treating an interface setting as proof of the complete control.
Understand how permissions reach the search system
Many assistants use a search index or another intermediate store. The source document's permission settings do not, by themselves, prove that every connected copy follows them. Ask which components hold the content and how each receives updated access information.
Document-level access can use different mechanisms, including security filters and identity-based controls. Ask the supplier to distinguish generally available features from any preview functionality used in the proposed configuration. Indexed permission metadata must be kept in step with source permissions. These details explain why a supplier must demonstrate the particular configuration and update process. Our permission-aware RAG knowledge search guide provides the related checks.
Turn that explanation into an operating question: after a source owner's permission decision changes, when does the assistant stop using the restricted content? Ask about indexed copies, retrieved fragments and any stored results. Agree how the change is checked and what happens if the normal update process fails. A clear business requirement gives the developer something concrete to implement.
Test allowed and denied cases deliberately
Create a small set of test records containing harmless, distinctive details. Use them to check the boundaries without exposing real confidential material unnecessarily. Define the intended result for each user role and each source before running the tests.
Include a permitted request, a request outside the role's authority and a request concerning another client. Test a source whose access has been removed and a document that has been withdrawn from the approved collection. Ask the developer to provide evidence of the retrieval decision as well as the assistant's visible answer. A refusal in the final text does not prove that restricted information was never retrieved.
Keep the test record with the access brief. Write down what was checked, the configuration involved, the result and any unresolved issue. Repeat relevant checks when roles, sources or connectors change. This makes permission verification part of maintenance rather than a one-off demonstration at launch.
Give changes a clear business owner
Information permissions are not purely a development concern. Somebody in the business needs authority to approve new sources, change the intended audience and withdraw outdated material. Name that person or role, and identify a backup who can act when they are unavailable.
Create a simple request process for adding information. The request should state the task it supports, its owner, its audience and its approval status. Ask whether an existing approved source already answers the need. This prevents the collection expanding through casual requests until nobody can explain its boundaries.
Review the assistant's operating record without retaining unnecessary private content. Useful records should help authorised staff investigate issues and understand changes. Agree what is recorded, who can see it and how it is managed with the relevant policy owner. The review process should be proportionate to the assistant's actual purpose and information.
Launch with a small, understandable boundary
Start with a narrow task and a well-maintained set of approved sources. Have the business owner review example answers for meaning and suitability, while the technical owner verifies retrieval and action controls. These checks support different parts of the same system, so one should not replace the other.
Explain the assistant's role to users. Tell them what it can help with, where an answer needs human confirmation and how to report a problem. Give staff a route for handling questions that fall outside the approved task. This helps avoid informal workarounds that bypass the agreed information process.
Giraffe Digital's digital strategy services provide a starting point for assessing where an assistant belongs in the customer journey and working process. The useful outcome is an assistant whose information access has a clear purpose, accountable owners and demonstrated boundaries that can be maintained as the business changes.
Frequently asked questions
How should we define the assistant's work and audience?
Describe a few useful tasks. For example, a website assistant could explain published service options and direct visitors to the relevant enquiry page. An internal assistant could help a team find approved operating instructions. Write the intended users and expected outputs beside each task. Avoid starting with a broad ambition such as "answer any business question". That makes it difficult to judge whether a document is necessary or whether an answer is appropriate. A clearer task lets the team ask which sources are needed, which facts must remain current and who should approve the resulting information. Distinguish finding information from making a decision. An assistant that summarises an approved process does not automatically have authority to offer a discount, accept a contractual change or make a commitment to a customer.
How should we separate public information from internal working material?
A public assistant should have a clear set of information approved for public use. Useful material might include published service explanations, contact routes and agreed answers to common questions. Keep the collection aligned with the website so the assistant does not describe a service or availability that the business no longer offers. An internal assistant needs a more detailed audience definition. "Staff" may include several roles with different access to client, finance or personnel information. Write specific examples of what each intended role may retrieve. Where client records are involved, include examples that distinguish one client's information from another's. Review personal and confidential information with the person responsible for your policies and information handling. Document the approved purpose, the minimum information needed and the relevant operating arrangements.
How should we understand how permissions reach the search system?
Many assistants use a search index or another intermediate store. The source document's permission settings do not, by themselves, prove that every connected copy follows them. Ask which components hold the content and how each receives updated access information. Document-level access can use different mechanisms, including security filters and identity-based controls. Ask the supplier to distinguish generally available features from any preview functionality used in the proposed configuration. Indexed permission metadata must be kept in step with source permissions. These details explain why a supplier must demonstrate the particular configuration and update process. Our permission-aware RAG knowledge search guide provides the related checks. Turn that explanation into an operating question: after a source owner's permission decision changes, when does the assistant stop using the restricted content?
How should we test allowed and denied cases deliberately?
Create a small set of test records containing harmless, distinctive details. Use them to check the boundaries without exposing real confidential material unnecessarily. Define the intended result for each user role and each source before running the tests. Include a permitted request, a request outside the role's authority and a request concerning another client. Test a source whose access has been removed and a document that has been withdrawn from the approved collection. Ask the developer to provide evidence of the retrieval decision as well as the assistant's visible answer. A refusal in the final text does not prove that restricted information was never retrieved. Keep the test record with the access brief. Write down what was checked, the configuration involved, the result and any unresolved issue.
How should we launch with a small, understandable boundary?
Start with a narrow task and a well-maintained set of approved sources. Have the business owner review example answers for meaning and suitability, while the technical owner verifies retrieval and action controls. These checks support different parts of the same system, so one should not replace the other. Explain the assistant's role to users. Tell them what it can help with, where an answer needs human confirmation and how to report a problem. Give staff a route for handling questions that fall outside the approved task. This helps avoid informal workarounds that bypass the agreed information process. Giraffe Digital's digital strategy services provide a starting point for assessing where an assistant belongs in the customer journey and working process.